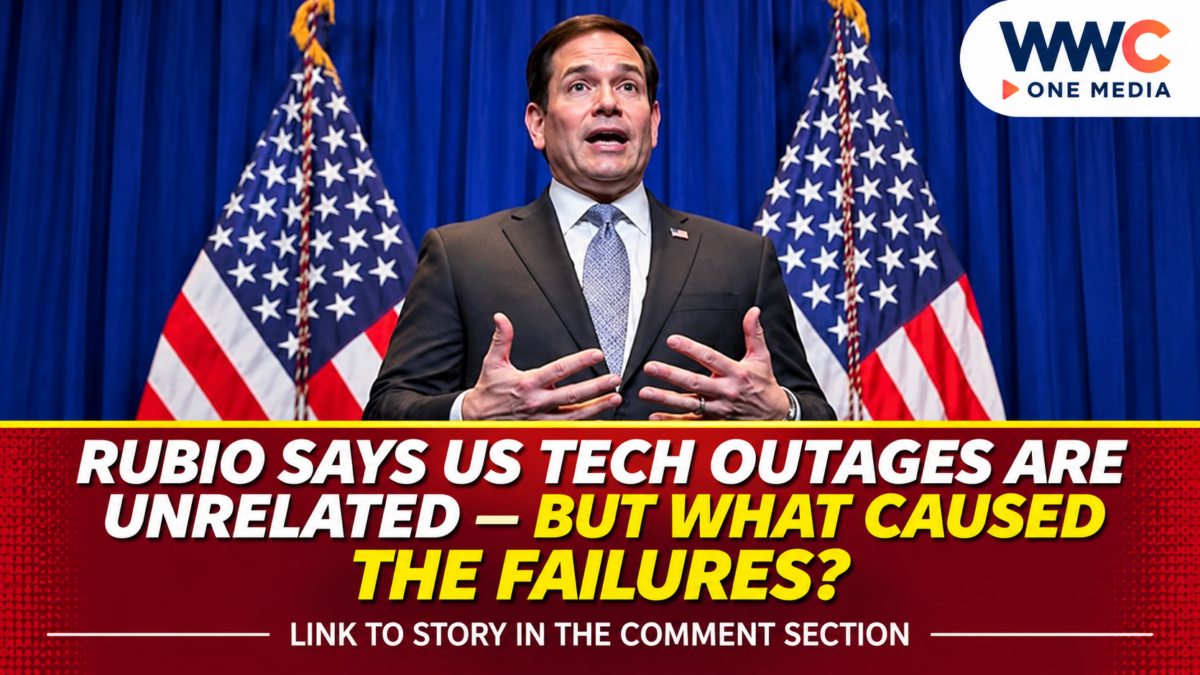
US Secretary of State Marco Rubio said during remarks to the press in Manila on Nov. 17, 2026, that the US government had found no evidence connecting a recent series of technology failures or attributing them to hostile actors. The disruptions included an aviation-wide ground stop, problems affecting Microsoft services and interruptions reported in banking systems.
The distinction matters because several serious breakdowns can occur close together without sharing a cause. Public safety and commercial continuity still depend on identifying what failed in each system, explaining the safeguards that worked and documenting the repairs.
US tech outages: what Rubio actually said
Rubio’s published press remarks addressed concerns that separate incidents might form part of a broader attack. He said the government had no information demonstrating that the Microsoft, Federal Aviation Administration (FAA) and banking incidents were linked. He also said the available evidence offered no reason to attribute them to cybercriminals or a foreign government.
Those comments describe the government’s information at the time of the briefing. They are not a public forensic report establishing the complete root cause of every failure. Rubio distinguished reassurance about the current evidence from the ongoing need to defend against genuine cyber threats.
The secretary also addressed questions about artificial intelligence. Rather than assigning AI a role in any particular outage, he declined to speculate about the incidents and directed detailed technical questions to affected organisations.
Why it matters: A lack of evidence of an attack should not be presented as proof that technology is immune to malicious interference. Equally, disruption alone is not evidence of sabotage. The appropriate standard is the incident-specific technical record.
FAA explains the aviation shutdown
The FAA’s Nov. 15 public explanation provides the clearest independently documented operational sequence among the events under discussion. A telecommunications problem on Nov. 13 led it to impose a nationwide ground stop at approximately 3:30 p.m. Eastern Time. Aircraft departures resumed after the system stabilised at 8:15 p.m.
The agency said instability affected 17 of 22 Air Route Traffic Control Centers and extended to some approach-control facilities. Its legacy telecommunications network experienced a surge of data traffic—about 1,000 connection attempts every four to five seconds—during routine equipment replacement work.
The FAA disabled particular router functionality and made precautionary changes to more than 60 other routers while continuing its investigation. It said approximately 3,500 aircraft already airborne landed safely and some radio frequencies and radar feeds continued functioning.
It also reported approximately 12,462 flight cancellations on Nov. 13, while explicitly warning that not all cancellations were directly attributable to the ground stop. This nuance prevents an inflated accounting of the incident’s direct impact.
WWC previously detailed the FAA’s network-failure findings. The new development is the government’s assessment that this aviation failure was not connected to the other disruptions.
Microsoft experienced a separate service failure
Microsoft’s public support channels recorded service-access problems affecting Microsoft 365 on Nov. 12. The company’s incident updates, discussed in its service-health communications, identified a technical disruption rather than attributing the event to malicious activity.
A technical outage can interrupt email, collaboration or authentication without demonstrating that someone accessed confidential data. An investigation into service availability and an investigation into a data breach ask different questions and can produce different findings.
WWC’s earlier Microsoft 365 restoration report addressed the gap between a provider marking a service restored and every customer’s workflows returning to normal. That distinction remains important for companies dependent on cloud software.
The public primary material reviewed for this article does not support a single common technical mechanism linking Microsoft’s infrastructure with the FAA’s telecommunications network. It would therefore be misleading to describe their simultaneous visibility as evidence of a shared attack.
Banking failures need their own evidence
Rubio included banking disruptions in his description of separate incidents, but the reviewed official remarks did not identify a definitive root cause for every bank or payment service affected. Without an authenticated institution-specific incident report, this article cannot assign one cause across the financial sector.
Customers can encounter similar symptoms—failed login attempts, unavailable transfers or delayed transactions—for different operational reasons. A bank’s underlying payments infrastructure may differ substantially from the infrastructure supporting commercial aviation or workplace email.
Analysis: The common feature is public dependence on digital services, not a proven common attacker. Organisations should explain which functions were interrupted, when service was restored and whether there is evidence of data compromise. These are more useful questions than speculating from coincidence.
Digital resilience is a business issue, not only a security issue
Rubio described how cyber defenders may discover and repair vulnerabilities while systems continue operating. Maintenance and configuration work can also create temporary service interruptions, a challenge demonstrated by the FAA’s published explanation.
The episode raises questions about operational resilience: whether systems have redundant communications, whether planned changes can be safely rolled back and how quickly operators can isolate malfunctioning components. Such questions apply even if an incident is not malicious.
WWC’s earlier report on the FAA ground stop’s impact on departures shows how disruptions can continue affecting schedules after core systems are stabilised. The same principle applies to digital commerce: recovery of the technology does not instantly reverse every downstream delay.
For Philippine organisations using international cloud, airline and financial systems, the practical lesson is to review business-continuity arrangements. The available evidence does not establish a separate nationwide technology incident in the Philippines arising from these US events.
What happens next
Investigators and service providers can strengthen the public record by releasing final incident reports, precise timelines, corrective actions and any further evidence concerning security. The FAA has disclosed technical findings and remedial steps; different organisations may publish details on different schedules.
Rubio’s conclusion was a statement about evidence available when he spoke, not a guarantee that future cyber incidents will never happen. The immediate challenge is to make each affected system more reliable and to communicate verified findings without creating unnecessary alarm.
FAQ
Were the recent US tech outages a coordinated cyberattack?
Rubio said the government had no evidence connecting the incidents to one another or to malicious actors when he spoke in Manila. That is the government’s stated assessment, not a final forensic report for every system.
What caused the FAA’s November 2026 ground stop?
The FAA identified telecommunications instability involving heavy connection traffic during routine equipment replacement. It implemented router changes while continuing its investigation.
Was Microsoft’s outage caused by hackers?
The Microsoft service communications reviewed characterised the incident as technical. The available record did not establish malicious activity as its cause.
Can a technology outage happen without a cyberattack?
Yes. Equipment, networking and configuration problems can interrupt services even without unauthorised access. Each incident requires its own investigation.