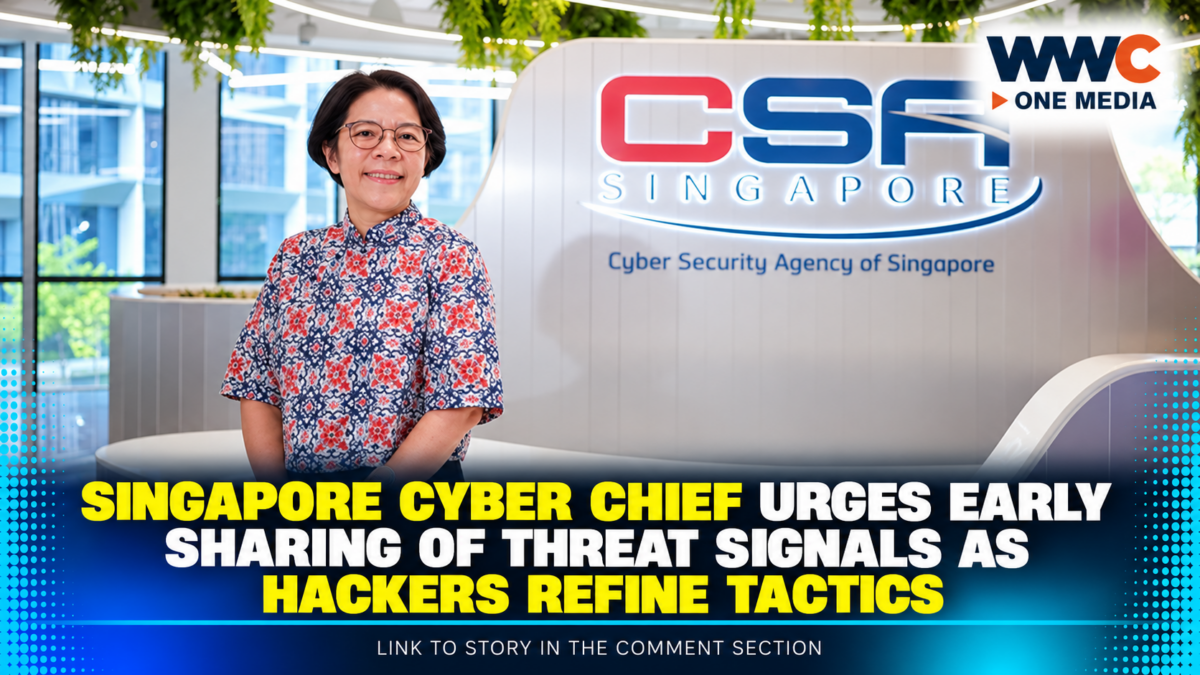
Singapore’s cybersecurity authorities are stressing the importance of sharing small, early warning signs of suspicious digital activity, warning that closer cooperation can help organisations detect emerging threats before they escalate into serious incidents.
As cyber threat actors refine their methods and increasingly use artificial intelligence (AI), cybersecurity experts say organisations cannot rely solely on detecting attacks after they have begun. Early information-sharing between agencies, businesses and critical infrastructure operators is becoming an increasingly important part of cyber defence.
The message from Singapore’s cybersecurity leadership comes amid a changing threat landscape in which attacks can develop faster, target specific organisations and exploit weaknesses across connected systems and supply chains.
Why Small Cybersecurity Signals Matter
Not every cyber incident begins with an obvious disruption. Unusual network activity, suspicious login attempts or unexpected system behaviour may appear insignificant when viewed in isolation.
However, information that seems minor to one organisation could help another identify a wider campaign or recognise a pattern of malicious activity.
Sharing these early indicators can help cybersecurity teams connect separate pieces of information, investigate potential risks and respond before an incident causes greater damage.
The approach depends on organisations being willing to report suspicious activity promptly rather than waiting until they have confirmed the full scale of a threat.
It also requires clear channels for sharing relevant information and coordinating responses, while protecting sensitive business and personal data.
AI Is Changing the Cyber Threat Landscape
Artificial intelligence is creating new opportunities for cyber defenders, but it is also giving malicious actors tools to operate at greater speed and scale.
Singapore’s Cyber Security Agency (CSA) said in its June 2026 Singapore Cyber Landscape report that AI is increasingly being used to support cyberattacks. It warned that emerging autonomous AI systems could automate parts of an attack process and shorten the time available for defenders to respond.
These developments make early detection and information-sharing more important. If attackers can identify weaknesses and move quickly, organisations may have less time to investigate unusual activity once an attack is underway.
AI is not the only concern. Cybersecurity teams must also contend with persistent threats, malicious infrastructure, ransomware and vulnerabilities in connected devices and systems.
The challenge is therefore not simply to acquire new technology, but to ensure that organisations can recognise threats, share relevant intelligence and act on it in time.
Singapore Moves Beyond Traditional Cyber Defences
Singapore has been strengthening its cybersecurity approach, including efforts to identify suspicious activity within systems rather than focusing exclusively on keeping attackers out.
In September, The Straits Times reported that the CSA and government technology agencies were developing and deploying in-house AI tools to help protect government systems following a cyberespionage incident involving Singapore’s major telecommunications operators.
The agency has also been working to improve the detection of potential entry points in critical information infrastructure, including weaknesses such as unpatched software and insecure configurations.
These measures reflect a broader shift towards more proactive cyber defence. Organisations increasingly need to look for signs that an attacker may already have gained access, while working to limit the opportunity for further intrusion.
No single tool can eliminate cyber risk. Effective protection also depends on trained personnel, timely reporting, coordination and consistent security practices.
Why Cooperation Between Organisations Is Essential
Cyber threats often cross organisational and national boundaries. A weakness in one service provider or supplier can create risks for other organisations that depend on its systems.
Information-sharing can help defenders understand whether an incident is isolated or connected to a broader campaign. It can also allow organisations to respond to known threats without having to discover every warning sign independently.
Singapore has been building cooperation between government agencies, critical infrastructure operators and industry partners as part of its wider cybersecurity strategy.
The CSA’s June report highlighted the need for collaboration across sectors to strengthen resilience against an increasingly complex, AI-enabled threat environment.
For businesses, this means cybersecurity should not be treated solely as an internal technical responsibility. Reporting mechanisms and trusted partnerships can help ensure that important information reaches the organisations best placed to act on it.
What This Means for Businesses and the Public
Organisations can strengthen their preparedness by ensuring employees know how to report suspicious digital activity, maintaining clear incident-response procedures and keeping systems updated.
They should also establish appropriate channels for sharing threat information with relevant cybersecurity teams and authorities, in line with applicable rules and confidentiality requirements.
For members of the public, basic digital security remains important. Keeping software updated, using strong and unique passwords, enabling multi-factor authentication where available and being cautious with unexpected messages can reduce exposure to common threats.
People should also report suspected scams or compromised accounts through the appropriate official channels rather than assuming that an incident is too minor to matter.
The Key Challenge: Acting Before a Threat Escalates
As cyber threat actors continue to adapt, Singapore’s emphasis on early warning signals reflects a central challenge for modern cybersecurity: useful information must reach the right people quickly enough to make a difference.
The effectiveness of that approach will depend on whether organisations can detect suspicious activity, communicate relevant findings and coordinate their responses without unnecessary delays.
Sharing an early warning does not guarantee that an attack will be prevented. But when combined with strong security practices, effective monitoring and timely action, it can give defenders a better opportunity to identify emerging threats before the consequences grow.
WWC ONE MEDIA G,A