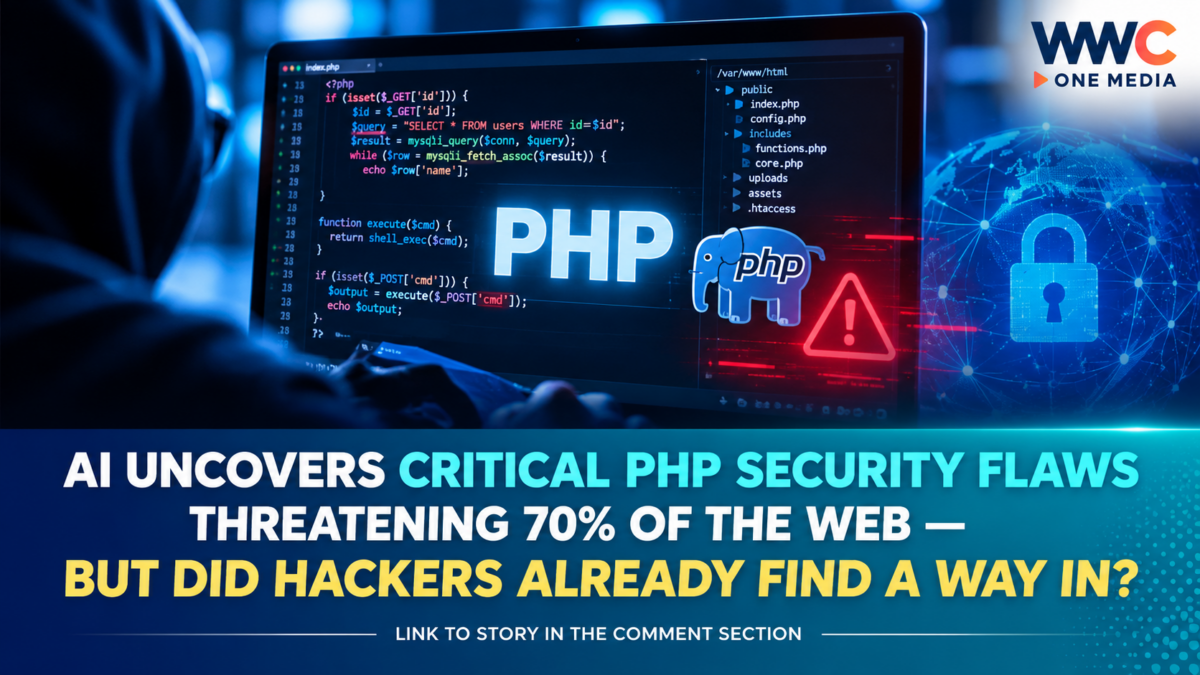
NEW YORK — Artificial intelligence may have helped prevent one of the most devastating cybersecurity incidents in recent internet history after researchers uncovered two critical vulnerabilities in PHP, the programming language used by an estimated 70% of websites worldwide.
The discovery, involving AI-powered security research and coordinated international action, has triggered an urgent global effort to protect government websites, businesses and online services from potentially catastrophic cyberattacks.
The vulnerabilities, collectively dubbed PHP2Shell, could allow attackers to execute malicious code remotely on vulnerable web servers without needing legitimate login credentials.
In practical terms, successful exploitation could give criminals unauthorized access to sensitive information, enable website manipulation or provide an entry point for further attacks.
But behind the alarming discovery is an unexpected development: the same artificial intelligence technology that cybersecurity experts fear could empower hackers may also be one of the strongest tools available to stop them.
Decade-old vulnerabilities threaten critical internet infrastructure
The security flaws were particularly troubling because the underlying weaknesses had existed in PHP for more than a decade.
PHP powers the server-side operations of millions of websites, including applications built using widely adopted web technologies.
Researchers at Wiz, the cybersecurity company owned by Google, described the findings as exceptionally severe because attackers could potentially exploit vulnerable servers without authentication.
Although approximately seven in ten websites use PHP, that does not mean 70% of all websites were confirmed exploitable. Actual exposure depends on software versions, configurations and whether security patches have been installed.
The distinction is important, but it does little to diminish the potential consequences for organizations still running affected systems.
AI helps researchers uncover what humans struggled to prove
The discovery marked a major milestone for artificial intelligence in cybersecurity.
In August 2026, researchers at Wiz and cybersecurity firm Calif independently identified serious PHP vulnerabilities with help from advanced AI systems.
Calif worked with OpenAI through an initiative called Patch the Planet, which brings together security researchers, technology companies and software maintainers to identify and address dangerous vulnerabilities before attackers can exploit them.
According to OpenAI, Calif used its GPT-5.6 Sol model to help uncover a critical security flaw.
Meanwhile, Wiz used AI-assisted security research to identify weaknesses that required unusually sophisticated technical analysis.
Rather than replacing human experts, the technology accelerated their ability to investigate complicated software behavior and validate potential attack methods.
Wiz reported that AI assistance enabled work that might otherwise have required an elite security team months to accomplish to be completed by a researcher in roughly a week.
The findings demonstrate how powerful AI tools can dramatically accelerate vulnerability discovery.
Governments and major websites scramble to respond
The October 21 public disclosure prompted urgent defensive action across multiple countries.
Some government websites and online services in Europe were temporarily taken offline while administrators investigated the vulnerabilities and implemented protective updates.
Parts of the BBC’s online services also underwent precautionary maintenance, while authorities in Japan urged organizations to act quickly.
In the United States, government cybersecurity officials assessed potential exposure and pushed for rapid mitigation.
Leading technology and infrastructure companies, including Cloudflare and Amazon Web Services, were informed during the coordinated response process.
PHP maintainers subsequently released security updates designed to address the vulnerabilities.
The operation highlighted the importance of responsible disclosure, in which researchers privately report weaknesses and allow developers to prepare patches before technical details become widely available.
Hackers begin probing for weaknesses
Despite the coordinated response, cybersecurity experts warned that publishing vulnerability details creates an opportunity for criminals to identify organizations that have failed to update their systems.
Cloudflare Chief Technology Officer Dane Knecht reported early attack activity targeting the newly disclosed weaknesses even before patches became publicly available.
This underscores a dangerous reality of modern cybersecurity: once a major vulnerability becomes known, attackers can rapidly begin searching for exposed systems.
The situation does not establish that a large-scale successful compromise has occurred. However, the combination of publicly available technical information and unpatched web servers presents an ongoing security risk.
Cybercriminals could potentially attempt to steal confidential records, interfere with business operations or use compromised systems to launch additional attacks.
Why AI could transform the global cybersecurity industry
The PHP2Shell discovery also challenges growing fears that AI might eventually make traditional cybersecurity companies obsolete.
Instead, the incident demonstrates why human expertise, security research and large-scale protective infrastructure may become more important as increasingly powerful AI tools emerge.
AI can rapidly analyze code, identify suspicious patterns and assist with vulnerability testing.
But human specialists still play a crucial role in determining whether findings are genuine, developing reliable fixes, coordinating disclosure and protecting operational systems.
The broader implications extend far beyond PHP.
As AI systems grow more capable, researchers may uncover previously hidden flaws in other widely used software, exposing risks that remained undetected for years.
This creates a difficult cybersecurity paradox.
The faster AI discovers vulnerabilities, the faster defenders must act — because malicious actors may be able to use similar technology to find and exploit those same weaknesses.
A deeper problem: Open-source software needs stronger protection
The incident has also renewed scrutiny of the resources available to maintain critical open-source technology.
Much of the internet depends on software maintained by relatively small teams, even when those projects support enormous commercial and government operations.
The PHP Foundation acknowledged that earlier indications of an underlying weakness had emerged before the 2026 disclosure, but technical complications and resource limitations delayed resolution.
The episode demonstrates that discovering vulnerabilities is only one part of the challenge.
Organizations also need experienced maintainers, sustainable funding, effective coordination and the capacity to release and deploy fixes quickly.
Without those investments, increasingly powerful vulnerability-detection tools could overwhelm already stretched security teams.
What businesses and website administrators should do
Cybersecurity specialists are urging organizations using PHP to review their infrastructure and ensure all affected installations have been updated.
Recommended measures include:
- Checking PHP versions against official security advisories.
- Applying the appropriate security patches immediately.
- Reviewing server logs for suspicious activity.
- Monitoring internet-facing applications for attempted exploitation.
- Working with hosting providers and cybersecurity teams to confirm that protections are active.
- Temporarily restricting vulnerable services when patches cannot be applied safely.
OpenAI has also released a Codex-based PHP version-checking tool to help organizations determine whether relevant updates may be necessary.
Security experts emphasize that temporary workarounds should not be treated as substitutes for properly installed security patches.
Has AI delivered its first major cybersecurity victory?
In a commentary published by Channel NewsAsia on October 24, Bloomberg Opinion columnist Dave Lee argued that the PHP incident represents one of the clearest victories yet for defenders in the emerging age of AI-powered cybersecurity.
The argument rests on a significant achievement: researchers discovered dangerous weaknesses, coordinated with software maintainers and infrastructure providers, and helped prepare protections before a potentially wider crisis unfolded.
Yet the outcome remains uncertain.
Security researchers still face the challenge of identifying vulnerable installations, monitoring exploitation attempts and ensuring organizations worldwide apply the necessary updates.
The discovery is therefore not proof that AI has solved cybersecurity.
Instead, it reveals a changing battlefield in which artificial intelligence can give defenders extraordinary capabilities while simultaneously lowering barriers for sophisticated attackers.
For now, researchers appear to have gained a critical head start. But as AI becomes capable of uncovering software weaknesses at unprecedented speed, one question remains: will defenders continue finding the flaws first — or will the next discovery give cybercriminals the advantage?