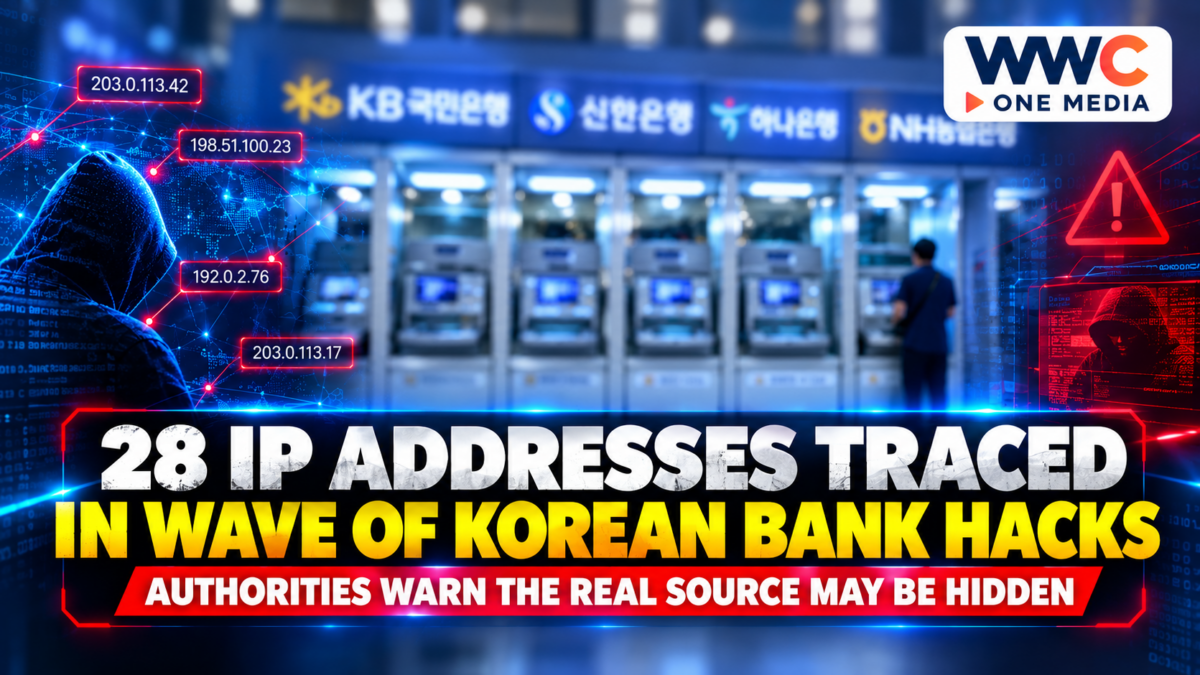
SEOUL — South Korea’s financial watchdog has identified 28 internet protocol (IP) addresses linked to a series of recent hacking attacks targeting financial institutions, as authorities race to determine the scope and origin of the growing cyber threat.
The Financial Supervisory Service (FSS) said the addresses were associated with hacking attempts against Korean financial companies and were traced across 12 countries and territories, including the United States, Japan, Hong Kong, Singapore, Vietnam, Thailand, Malaysia, Spain, Latvia, Sweden, Germany and South Korea.
However, officials stressed that the locations of the IP addresses should not be interpreted as proof of the attackers’ nationality or actual location. Hackers can route activity through systems in different countries to make their origins harder to identify.
The development follows a string of cyber incidents involving major Korean financial institutions.
Shinhan Bank reported that personal information belonging to about 25,000 customers had been exposed, including names, phone numbers and annual income. Hana Bank also reported a leak involving personal information from 89 customers. Meanwhile, Woori Bank and NH Nonghyup Bank detected similar unauthorized access attempts but said their defenses prevented confirmed information leaks.
Authorities believe some of the attacks may have involved AI-assisted hacking techniques, adding a new layer to concerns over the ability of attackers to rapidly search for vulnerabilities.
South Korean President Lee Jae Myung has called for a thorough investigation after authorities reported signs that AI models may have been used in some of the attacks. Police have since opened a formal investigation into the incidents.
The FSS has distributed the identified IP addresses and related threat information across the financial sector. Institutions have been instructed to inspect externally accessible IT systems, identify vulnerabilities and strengthen authentication and access controls.
Financial companies have also been asked to verify whether suspicious IP addresses have been blocked and whether their systems show evidence of related intrusion attempts. The regulator set Oct. 8 as the deadline for institutions to complete their internal security checks and address identified weaknesses.
The investigation comes as cybersecurity concerns spread beyond banks. Brokerage firms, insurers and credit-card companies are also reviewing their systems amid fears that attackers may have been scanning multiple financial institutions for vulnerabilities rather than targeting only one company.
For investigators, the 28 IP addresses could provide important clues. But they are only part of a much larger puzzle.
The key question now is not simply where those digital traces appeared — but who was actually behind the attacks and whether the same campaign is still active.
WWC ONE MEDIA G,A