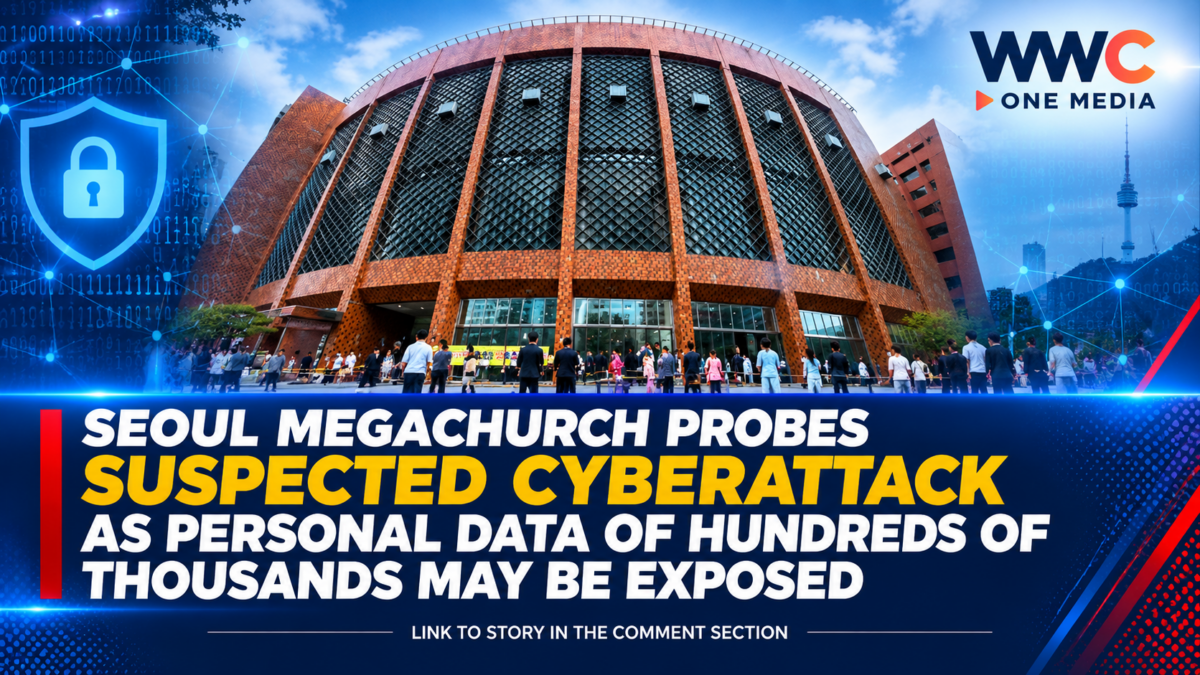
SEOUL, South Korea — One of South Korea’s largest churches is investigating a suspected cyberattack that may have exposed personal information involving hundreds of thousands of its members, adding a religious institution to a growing series of cybersecurity incidents in the country.
Yoido Full Gospel Church said Wednesday that it had been notified by the Korea Internet & Security Agency (KISA) of suspected unauthorized access to its information systems. The church immediately began an emergency security review and brought in outside cybersecurity specialists to examine the suspected data and system access records.
The church said its investigation found that one file containing membership-information change histories included personal information associated with approximately 850,000 members.
The information included names, dates of birth and records of changes to membership information. The church said the file also contained 2,629 records involving changes to resident registration numbers, 3,964 phone-number changes and 7,202 address changes.
The church said it is notifying affected members in accordance with relevant laws and procedures.
Investigation Into the Full Scope Continues
The scale of the incident remains under investigation, and different figures have emerged depending on what investigators are measuring.
Cybersecurity company Oasis Security previously reported finding a much larger collection of data apparently originating from Yoido Full Gospel Church on an overseas server associated with an attacker. Its analysis identified roughly 960,000 member-information records updated over the previous two years, along with about 330,000 records related to offerings and other internal documents.
The church has emphasized that it is still verifying the circumstances and extent of any actual unauthorized disclosure. The distinction is important because the presence of information on an attacker-controlled server does not by itself establish that every piece of data was accessed or used by an attacker.
Yoido Full Gospel Church said it had blocked external access to its systems, changed server passwords and was working with security specialists to identify vulnerabilities and strengthen its defenses. It also plans to replace its existing firewall.
Senior Pastor Lee Young-hoon apologized to members and said the church would cooperate with authorities while strengthening its information-protection systems.
Another Seoul Church Also Targeted
The incident is not isolated.
Cybersecurity investigators also found suspected attack-related information connected to Sarang Community Church in Seoul’s Seocho District. Data reportedly found on an attacker-controlled server included information involving about 89,000 church members and 286 employees and officials.
Investigators have found indications that different technical weaknesses may have been exploited at the two churches. In the Yoido case, researchers reported signs consistent with an intrusion through an ERP server, while the Sarang case involved suspected misuse of previously obtained credentials and weaknesses connecting internal systems.
Possible AI Connection Raises New Questions
The attacks are also attracting attention because investigators found signs suggesting that AI tools may have been used during parts of the intrusion.
Reuters reported that cybersecurity investigators found evidence suggesting AI-assisted tools may have played a role, although the precise methods and identities of those responsible remain under investigation.
Investigators examining attack logs reportedly found references to a “sub-agent” and structured reports documenting attack results, system structures and credentials. Security researchers believe such evidence may indicate automated or AI-assisted analysis, but it does not by itself establish exactly which AI system was used or who operated it.
The incidents come as South Korea is already dealing with a series of cyberattacks affecting financial institutions and other organizations, intensifying concerns about how attackers are using automation and emerging technologies.
A Wider Cybersecurity Warning
The church attacks highlight another potential vulnerability: large religious organizations can maintain extensive databases containing personal information even though their cybersecurity structures may differ from those of major corporations.
Security researchers have urged organizations to examine how systems such as membership databases, accounting platforms, human-resources systems and internal communications tools are connected, because a compromise of one system can potentially provide a pathway into others.
For Yoido Full Gospel Church, however, the immediate priority remains determining exactly what happened, what information was actually accessed and whether members face further risks.
As investigators continue tracing the suspected intrusion, the biggest question is no longer simply whether a cyberattack occurred — it is how much information was actually exposed and whether the same attackers targeted other organizations.
WWC ONE MEDIA G,A