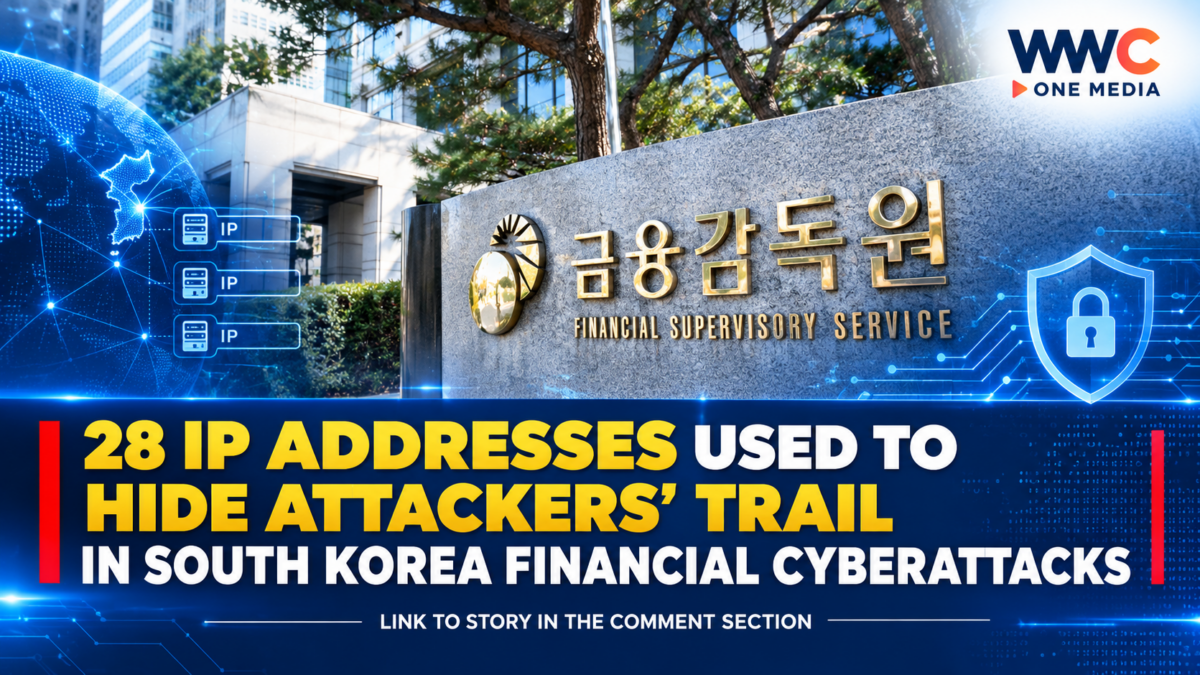
SEOUL, South Korea — A growing cyberattack investigation in South Korea has uncovered a network of 28 IP addresses across 12 countries, but authorities say the trail may be deliberately misleading.
Investigators have determined that many of the internet addresses connected to recent attacks on South Korean financial institutions were being used as relay points, making it harder to identify where the attacks actually originated.
The discovery adds another layer to an investigation already raising concerns over the use of advanced artificial intelligence tools in attacks against financial companies.
The Financial Supervisory Service identified the 28 addresses after analyzing suspected attacks involving several financial institutions. The addresses were linked to locations including the United States, Japan and 10 other countries. However, authorities have warned that an IP address does not necessarily reveal the nationality or physical location of the person behind an attack.
Hackers May Have Used Multiple Relay Points
Police investigating the incidents found evidence that multiple intermediate connections may have been used to conceal the attackers’ actual route.
That means the international spread of the IP addresses should not automatically be interpreted as evidence that hackers in those countries carried out the attacks.
Instead, investigators are working to reconstruct the actual intrusion path and identify the people or group responsible. International cooperation is also being pursued as part of the investigation.
Financial Firms Already Hit
The investigation follows a series of attacks and attempted intrusions involving South Korean financial companies.
Shinhan Bank reported that information belonging to approximately 25,000 customers had been exposed, including names, phone numbers and annual income. Hana Bank also reported the exposure of personal information belonging to 89 customers.
Other institutions, including Woori Bank and NH Nonghyup Bank, detected similar attempts but were able to block unauthorized access without confirmed personal-information leaks.
The attacks have prompted financial companies to conduct emergency security checks, particularly on externally accessible systems, authentication procedures and access controls.
AI Adds a New Dimension
The investigation has also focused on indications that attackers may have used AI-assisted tools to identify vulnerabilities.
South Korean authorities are examining whether AI agents were involved in some of the attacks, while officials have warned that emerging technologies could allow attackers to identify weaknesses more quickly and automate portions of cyber intrusions.
The Financial Services Commission has instructed financial companies to strengthen defenses and rapidly share threat information, including suspicious IP addresses and attack methods.
Authorities are also emphasizing that simply blocking identified addresses is not enough. Financial institutions have been ordered to examine externally exposed IT assets and check for vulnerabilities that could provide attackers with alternative routes into their systems.
The Biggest Question Remains
For investigators, the 28 IP addresses may be only the visible layer of a much larger operation.
Because many of the addresses appear to have been used to disguise the attackers’ actual path, identifying the countries associated with the connections does not necessarily identify the people responsible.
The investigation therefore continues to focus on reconstructing the attack chain and determining who ultimately controlled the intrusions.
As South Korea’s financial sector races to close potential security gaps, investigators now face a more difficult question: if the 28 IP addresses were only a cover, where did the attacks really begin?
WWC ONE MEDIA G,A