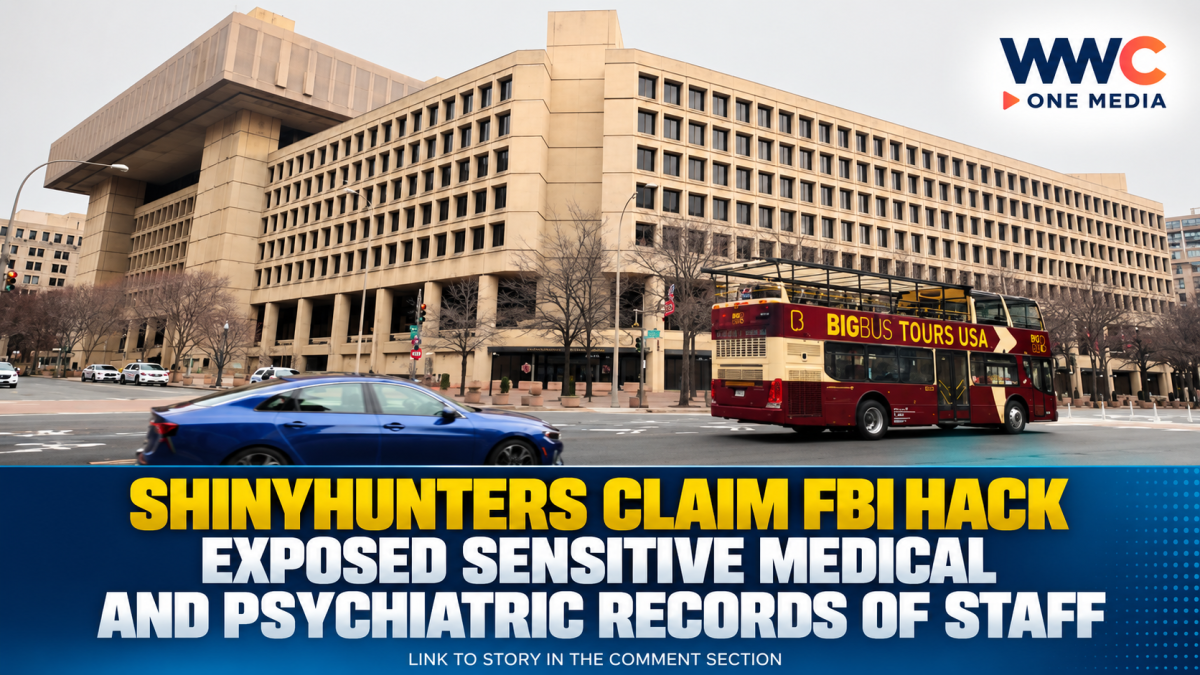
WASHINGTON — A cyberattack claimed by the hacking group ShinyHunters has reportedly exposed highly sensitive information belonging to FBI personnel, including medical and psychiatric evaluation records, raising new concerns about the security of employee data within the US law-enforcement agency.
The hackers first claimed on Sept. 22 that they had breached FBI systems and stolen information involving thousands of bureau employees. The group later alleged that the stolen material included detailed personnel information as well as medical and psychiatric records.
Some of the material provided by the hackers to journalists has been partially authenticated. Documents reviewed included sensitive medical and psychiatric evaluations, although the full origin, completeness and scope of the allegedly stolen dataset remain under investigation.
The FBI has confirmed that it is investigating unauthorized activity involving the FBIJobs.gov portal and the possible exposure of employee personal information. The bureau has not established publicly how far the intrusion reached or whether all of the data claimed by ShinyHunters was actually obtained from FBI systems.
The incident is particularly sensitive because FBI employees can hold positions involving counterintelligence, organized crime, terrorism and other investigations. Earlier reporting on the breach indicated that information allegedly obtained by the hackers included details about employees, their assignments and sensitive investigative work.
ShinyHunters is a well-known cybercriminal group associated with large-scale data theft and extortion campaigns. The group has previously attracted attention by publicly claiming responsibility for breaches and releasing or threatening to release stolen information.
The latest incident also illustrates the risks created when employee databases contain both routine personnel information and highly sensitive medical or security-related records. Such data can potentially expose individuals to identity theft, targeted fraud, harassment or other security risks if its authenticity and provenance are confirmed.
However, the hackers’ claims should not automatically be treated as proof that every piece of information they say they obtained came directly from FBI infrastructure. Investigators still have to establish the initial point of access, what systems were compromised and exactly how much information was taken.
The FBI has said it is aggressively investigating the reported breach. The agency’s findings will be important in determining whether the incident was limited to a particular portal or involved wider access to government systems and employee databases.
The breach comes amid a broader wave of cyberattacks targeting government agencies and other sensitive organisations. US authorities have separately investigated and disrupted hacking campaigns involving federal networks, highlighting the continuing difficulty of protecting systems containing valuable personnel and intelligence information.
For the FBI, the immediate challenge is not only determining what the hackers accessed but also identifying whether compromised employee information could create additional security risks.
The bigger concern now is whether the ShinyHunters claims will ultimately be confirmed as a large-scale compromise of sensitive FBI personnel records—or whether the investigation will show that the hackers overstated the scope of their access.